DevSecOps — Cybersecurity News

Latest News

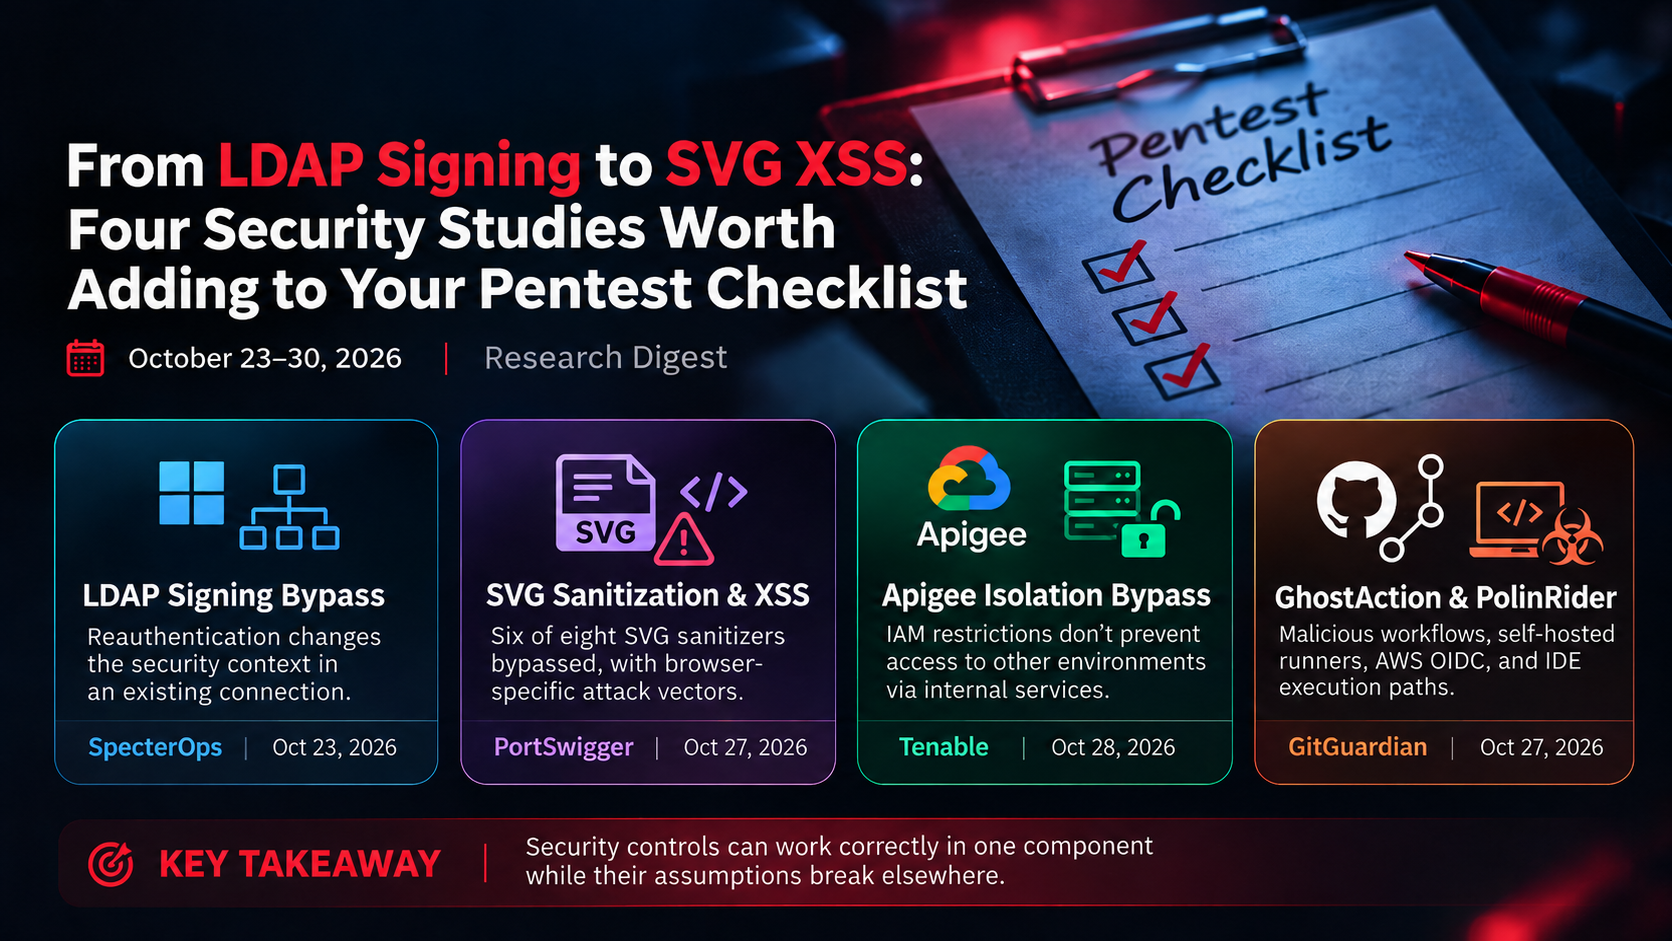
From LDAP Signing Bypass to SVG XSS: Four Security Research Studies Worth Adding to Your Pentest Checklist

From LDAP Signing Bypass to SVG XSS: Four Security Research Studies Worth Adding to Your Pentest Checklist

RedSide Security October 31, 2026 Penetration Testing 158 views

Four new cybersecurity studies reveal security control weaknesses involving LDAP signing bypasses, SVG sanitization and XSS, Google Cloud Apigee environment isolation, and GhostAction supply chain attacks. Explore the technical findings, exploitation prerequisites, and practical penetration testing lessons from SpecterOps, PortSwigger, Tenable, and GitGuardian.

Continue reading: From LDAP Signing Bypass to SVG XSS: Four Security…
Node2Shell (CVE-2026-111497) - We built an open-source scanner and a hands-on lab

Node2Shell (CVE-2026-111497) - We built an open-source scanner and a hands-on lab

RedSide Security October 30, 2026 Tools & Technology 465 views

RedSide Security has released an open-source Node2Shell (CVE-2026-111497) scanner and Docker-based testing lab. The toolkit features non-destructive, behavior-based detection, vulnerable and patched test environments, and a lightweight Python implementation to help security teams investigate potential exposure to the critical Brotli vulnerability.

Continue reading: Node2Shell (CVE-2026-111497) - We built an open-so…
RedSide Security Releases Open-Source PHP2Shell Testing Lab, Scanner, and RCE Verifier

RedSide Security Releases Open-Source PHP2Shell Testing Lab, Scanner, and RCE Verifier

RedSide Security October 29, 2026 Tools & Technology 184 views

RedSide Security has open-sourced a PHP2Shell security research toolkit featuring a realistic Docker lab, non-destructive vulnerability scanner, blind RCE verifier, and binary offset tooling. The project helps security professionals investigate CVE-2026-109618 and CVE-2026-109619 through practical, authorized testing.

Continue reading: RedSide Security Releases Open-Source PHP2Shell Te…
F5 Discloses High-Severity NGINX Vulnerabilities, Including Potential RCE Flaw

F5 Discloses High-Severity NGINX Vulnerabilities, Including Potential RCE Flaw

RedSide Security July 16, 2026 Vulnerability 207 views

F5 has released patches for three vulnerabilities affecting NGINX Plus and NGINX Open Source, including a critical heap buffer overflow (CVE-2026-42533) that may enable remote code execution. Organizations using NGINX web servers, ingress controllers, or gateway products should patch immediately and review affected configurations.

Continue reading: F5 Discloses High-Severity NGINX Vulnerabilities, …
 Jscrambler npm Package Compromised - Malicious Releases Deploy Cross-Platform Infostealer

Jscrambler npm Package Compromised - Malicious Releases Deploy Cross-Platform Infostealer

RedSide Security July 13, 2026 Vulnerability 209 views

Attackers compromised the Jscrambler npm package and published multiple malicious versions containing a cross-platform Rust infostealer. The malware targets cloud credentials, GitHub tokens, AI coding tools, cryptocurrency wallets, and CI/CD environments, highlighting the growing risk of software supply chain attacks against developers.

Continue reading: Jscrambler npm Package Compromised - Malicious Re…
Introducing CVEAlertor: Now With Public PoC & Exploit Monitoring

Introducing CVEAlertor: Now With Public PoC & Exploit Monitoring

RedSide Security July 02, 2026 Tools & Technology 287 views

CVEAlertor now monitors GitHub for newly released proof-of-concept exploits tied to tracked vulnerabilities. Security teams receive instant Telegram alerts when new CVEs are published and when public exploit code becomes available, helping prioritize patching before attackers strike.

Continue reading: Introducing CVEAlertor: Now With Public PoC & Expl…
Critical Cursor IDE Flaws Enable Full Sandbox Escape and Remote Code Execution

Critical Cursor IDE Flaws Enable Full Sandbox Escape and Remote Code Execution

RedSide Security July 01, 2026 Vulnerability 268 views

Two critical vulnerabilities in Cursor IDE, tracked as CVE-2026-50548 and CVE-2026-50549, allow attackers to escape the platform's sandbox and achieve full remote code execution through prompt injection. The flaws demonstrate how AI-driven coding agents can expose traditional software attack surfaces, leading to system compromise without user approval.

Continue reading: Critical Cursor IDE Flaws Enable Full Sandbox Esca…
GuardFall Bypass Lets Attackers Evade AI Coding Agent Safety Checks Using Decades-Old Shell Tricks

GuardFall Bypass Lets Attackers Evade AI Coding Agent Safety Checks Using Decades-Old Shell Tricks

RedSide Security June 30, 2026 Cybersecurity 289 views

Researchers have disclosed GuardFall, a shell command bypass technique that defeats safety protections in 10 popular AI coding agents. The flaw allows malicious commands to evade text-based filters and execute with user privileges, potentially exposing credentials, source code, and cloud infrastructure.

Continue reading: GuardFall Bypass Lets Attackers Evade AI Coding Ag…