RedSide Security — Cybersecurity News

Latest News

Introducing ReD-Pot: Open-Source Honeypot and Deception Platform for Detecting Attackers Inside Your Network

Introducing ReD-Pot: Open-Source Honeypot and Deception Platform for Detecting Attackers Inside Your Network

RedSide Security November 16, 2026 Tools & Technology 149 views

RedSide Security releases ReD-Pot Community Edition, a free, open-source honeypot and deception platform for detecting attackers inside enterprise networks. Featuring realistic decoy servers, honeytokens, lateral movement detection, attack-path visualization, MITRE ATT&CK mappings, and SIEM integration, ReD-Pot helps security teams identify suspicious activity after the initial compromise.

Continue reading: Introducing ReD-Pot: Open-Source Honeypot and Dece…
RedSide Security Releases ProcSnap: Open-Source Linux Incident Response and Threat Hunting Tool

RedSide Security Releases ProcSnap: Open-Source Linux Incident Response and Threat Hunting Tool

RedSide Security November 03, 2026 Tools & Technology 246 views

RedSide Security has released ProcSnap, a free, open-source Linux incident response and threat hunting tool featuring approximately 130 MITRE ATT&CK-mapped checks. Built with Python's standard library, ProcSnap helps security teams investigate suspicious processes, rootkits, persistence mechanisms, and authentication activity while collecting forensic evidence and generating self-contained HTML reports.

Continue reading: RedSide Security Releases ProcSnap: Open-Source Li…
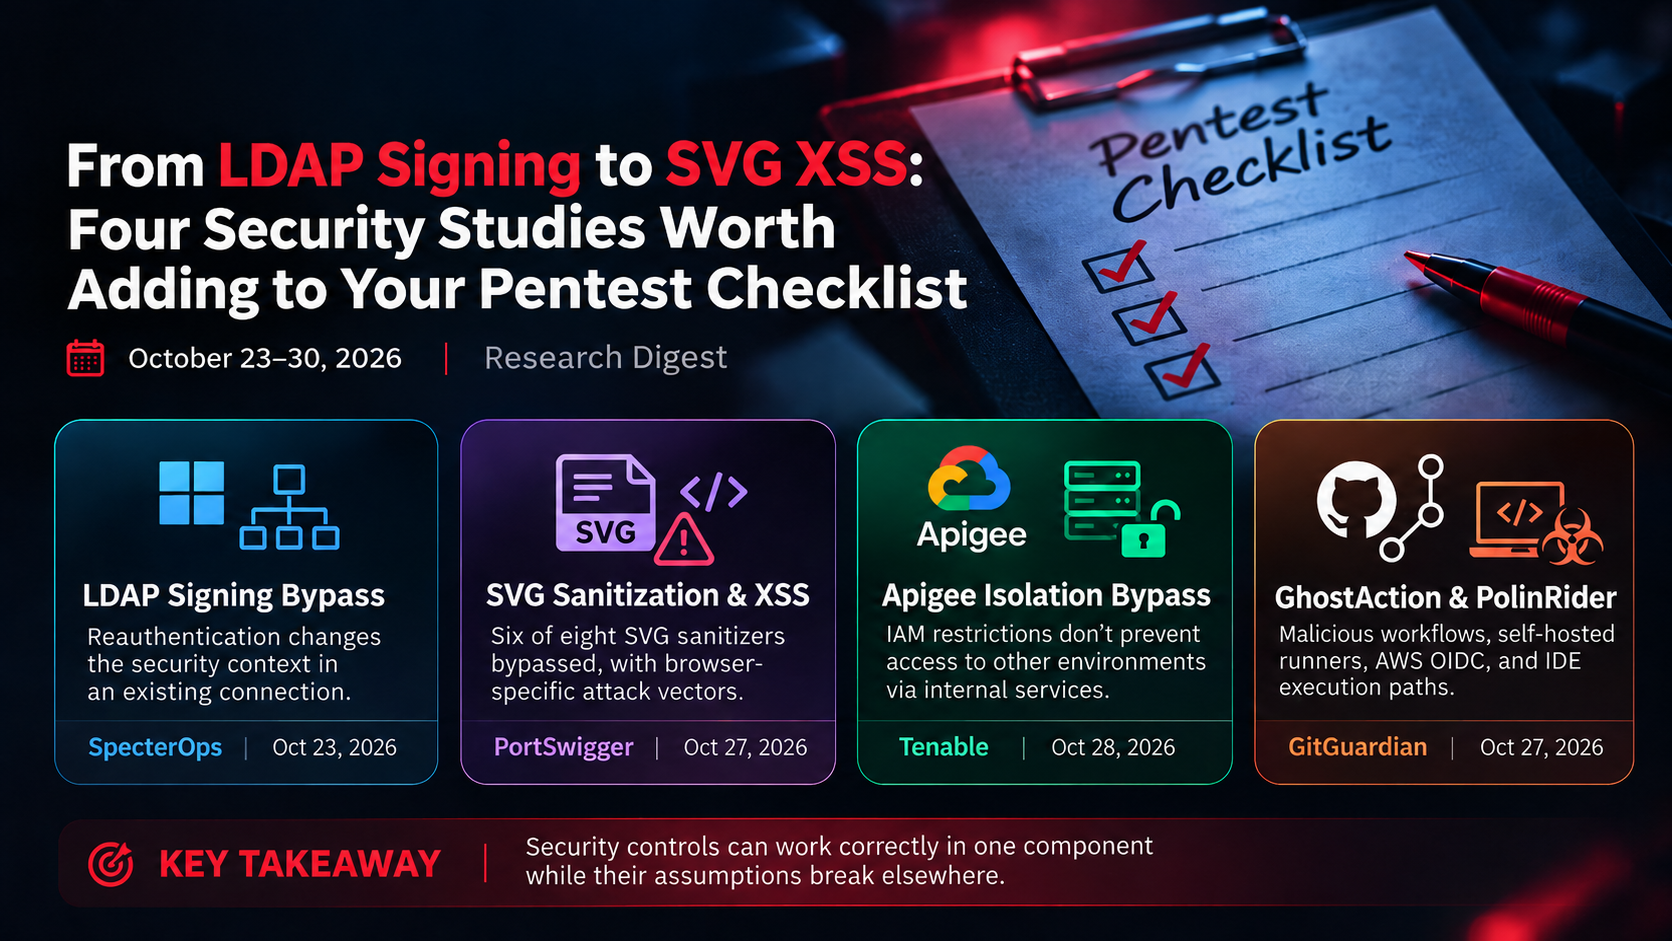
From LDAP Signing Bypass to SVG XSS: Four Security Research Studies Worth Adding to Your Pentest Checklist

From LDAP Signing Bypass to SVG XSS: Four Security Research Studies Worth Adding to Your Pentest Checklist

RedSide Security October 31, 2026 Penetration Testing 158 views

Four new cybersecurity studies reveal security control weaknesses involving LDAP signing bypasses, SVG sanitization and XSS, Google Cloud Apigee environment isolation, and GhostAction supply chain attacks. Explore the technical findings, exploitation prerequisites, and practical penetration testing lessons from SpecterOps, PortSwigger, Tenable, and GitGuardian.

Continue reading: From LDAP Signing Bypass to SVG XSS: Four Security…
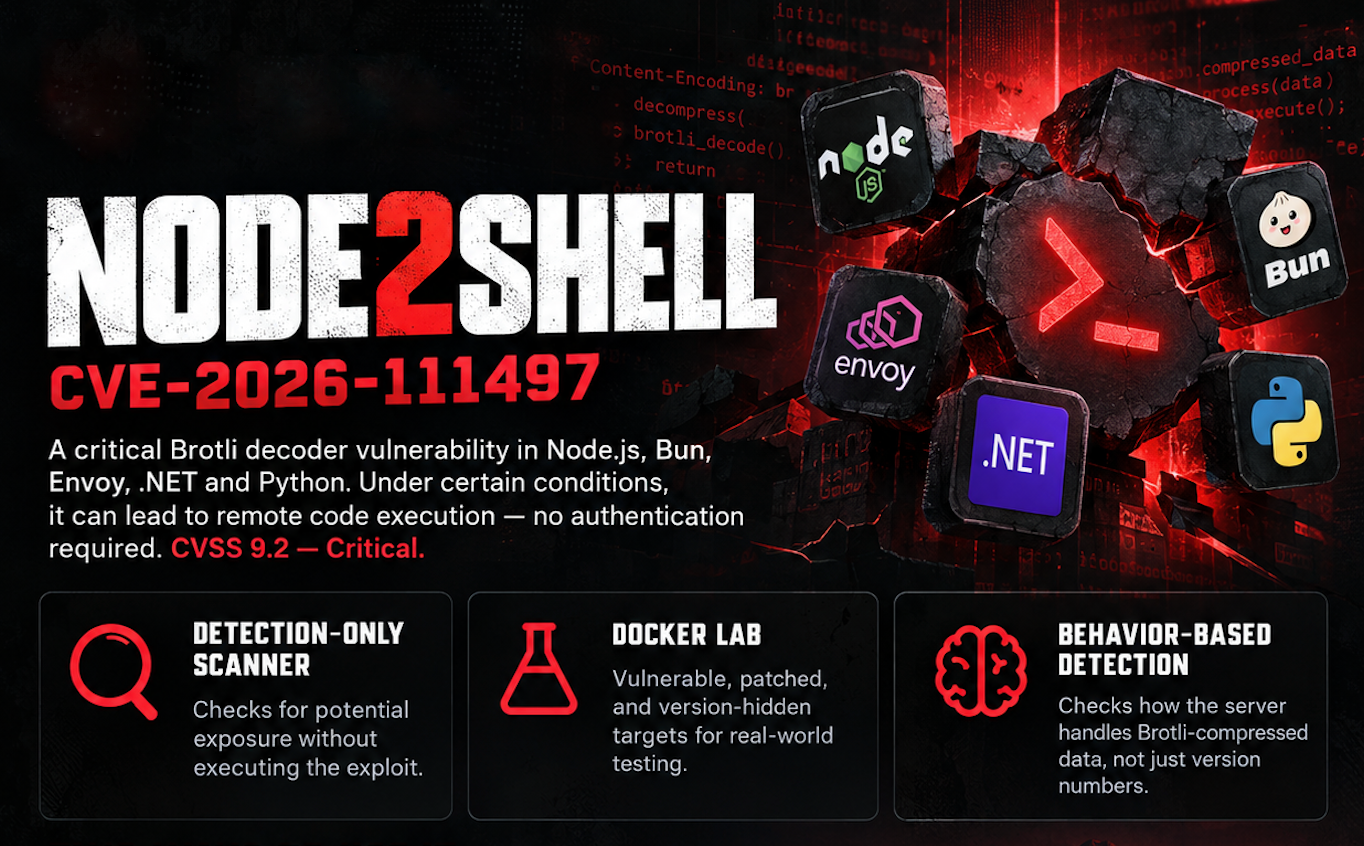
Node2Shell (CVE-2026-111497) - We built an open-source scanner and a hands-on lab

Node2Shell (CVE-2026-111497) - We built an open-source scanner and a hands-on lab

RedSide Security October 30, 2026 Tools & Technology 465 views

RedSide Security has released an open-source Node2Shell (CVE-2026-111497) scanner and Docker-based testing lab. The toolkit features non-destructive, behavior-based detection, vulnerable and patched test environments, and a lightweight Python implementation to help security teams investigate potential exposure to the critical Brotli vulnerability.

Continue reading: Node2Shell (CVE-2026-111497) - We built an open-so…
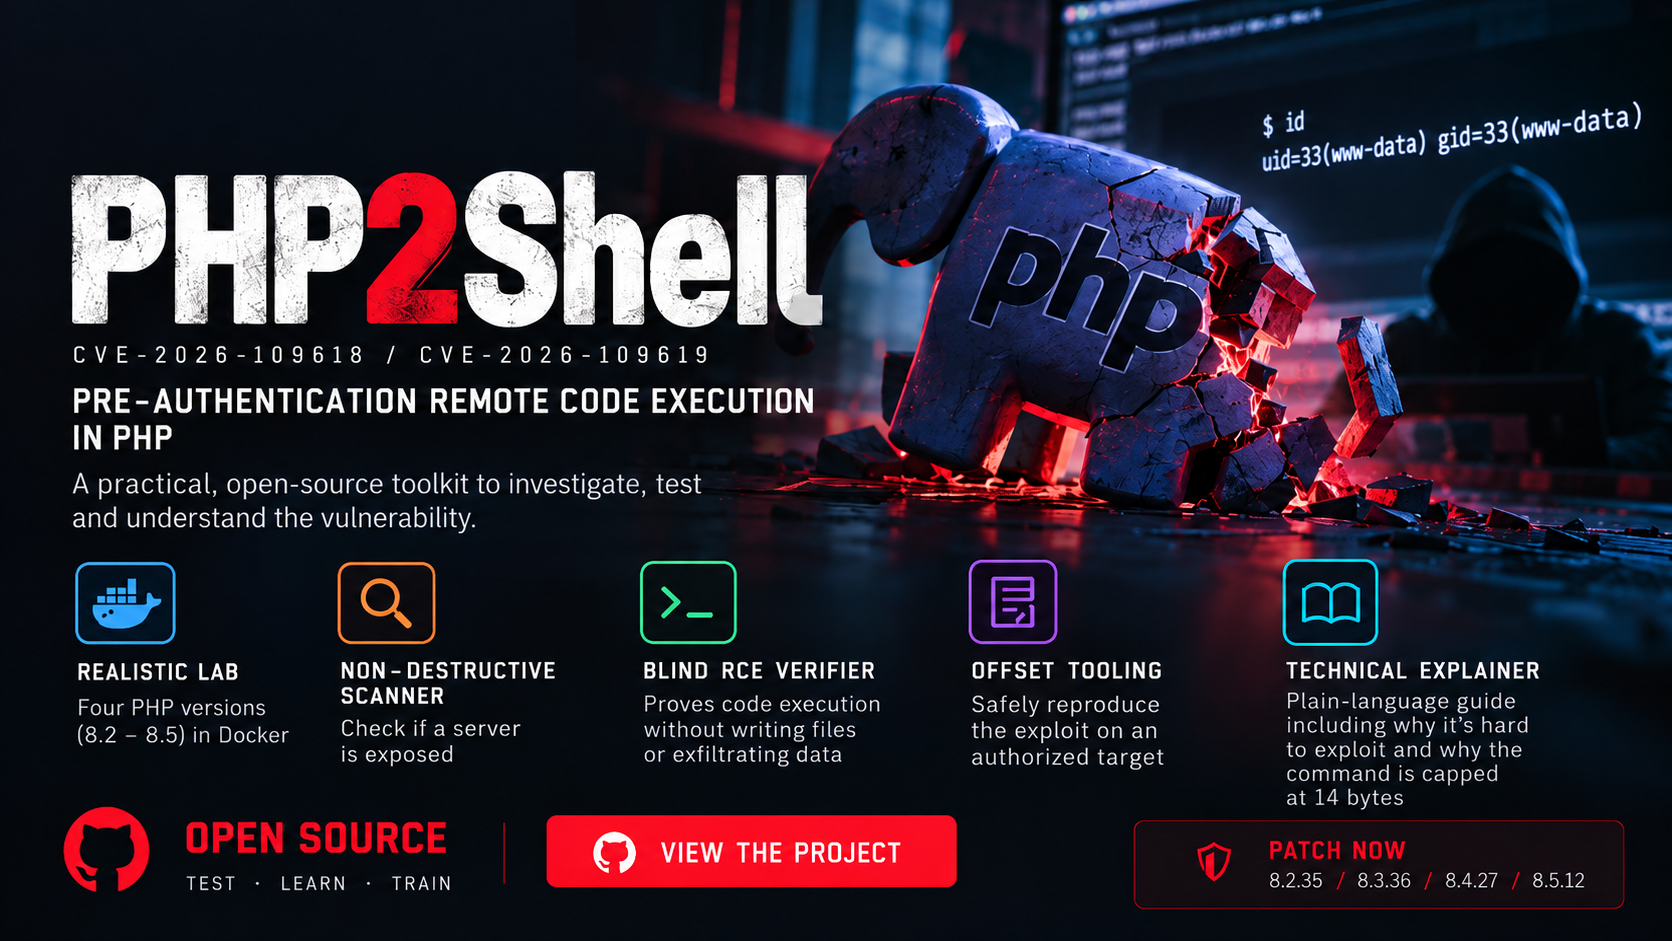
RedSide Security Releases Open-Source PHP2Shell Testing Lab, Scanner, and RCE Verifier

RedSide Security Releases Open-Source PHP2Shell Testing Lab, Scanner, and RCE Verifier

RedSide Security October 29, 2026 Tools & Technology 184 views

RedSide Security has open-sourced a PHP2Shell security research toolkit featuring a realistic Docker lab, non-destructive vulnerability scanner, blind RCE verifier, and binary offset tooling. The project helps security professionals investigate CVE-2026-109618 and CVE-2026-109619 through practical, authorized testing.

Continue reading: RedSide Security Releases Open-Source PHP2Shell Te…
Introducing AnyStix: Automated Country-Based Threat Intelligence for OpenCTI

Introducing AnyStix: Automated Country-Based Threat Intelligence for OpenCTI

RedSide Security July 02, 2026 Tools & Technology 235 views

AnyStix is an open-source threat intelligence tool that collects country-specific malicious submissions from ANY.RUN, enriches them with indicators, converts them into STIX 2.1 format, and automatically imports them into OpenCTI. The platform enables continuous, region-focused threat intelligence collection using publicly available sandbox data.

Continue reading: Introducing AnyStix: Automated Country-Based Threa…
Introducing CVEAlertor: Now With Public PoC & Exploit Monitoring

Introducing CVEAlertor: Now With Public PoC & Exploit Monitoring

RedSide Security July 02, 2026 Tools & Technology 287 views

CVEAlertor now monitors GitHub for newly released proof-of-concept exploits tied to tracked vulnerabilities. Security teams receive instant Telegram alerts when new CVEs are published and when public exploit code becomes available, helping prioritize patching before attackers strike.

Continue reading: Introducing CVEAlertor: Now With Public PoC & Expl…
Why RedSide Security is Armenia's Top Cybersecurity Company

Why RedSide Security is Armenia's Top Cybersecurity Company

RedSide Security June 28, 2026 RedSide Security News 223 views

RedSide Security is helping organizations across Armenia strengthen their cybersecurity posture through penetration testing, security assessments, incident response, and exposure monitoring. Discover why businesses trust RedSide Security to protect their critical assets and infrastructure.

Continue reading: Why RedSide Security is Armenia's Top Cybersecurit…