Web Application Security — Cybersecurity News

Latest News

From LDAP Signing Bypass to SVG XSS: Four Security Research Studies Worth Adding to Your Pentest Checklist

From LDAP Signing Bypass to SVG XSS: Four Security Research Studies Worth Adding to Your Pentest Checklist

RedSide Security October 31, 2026 Penetration Testing 182 views

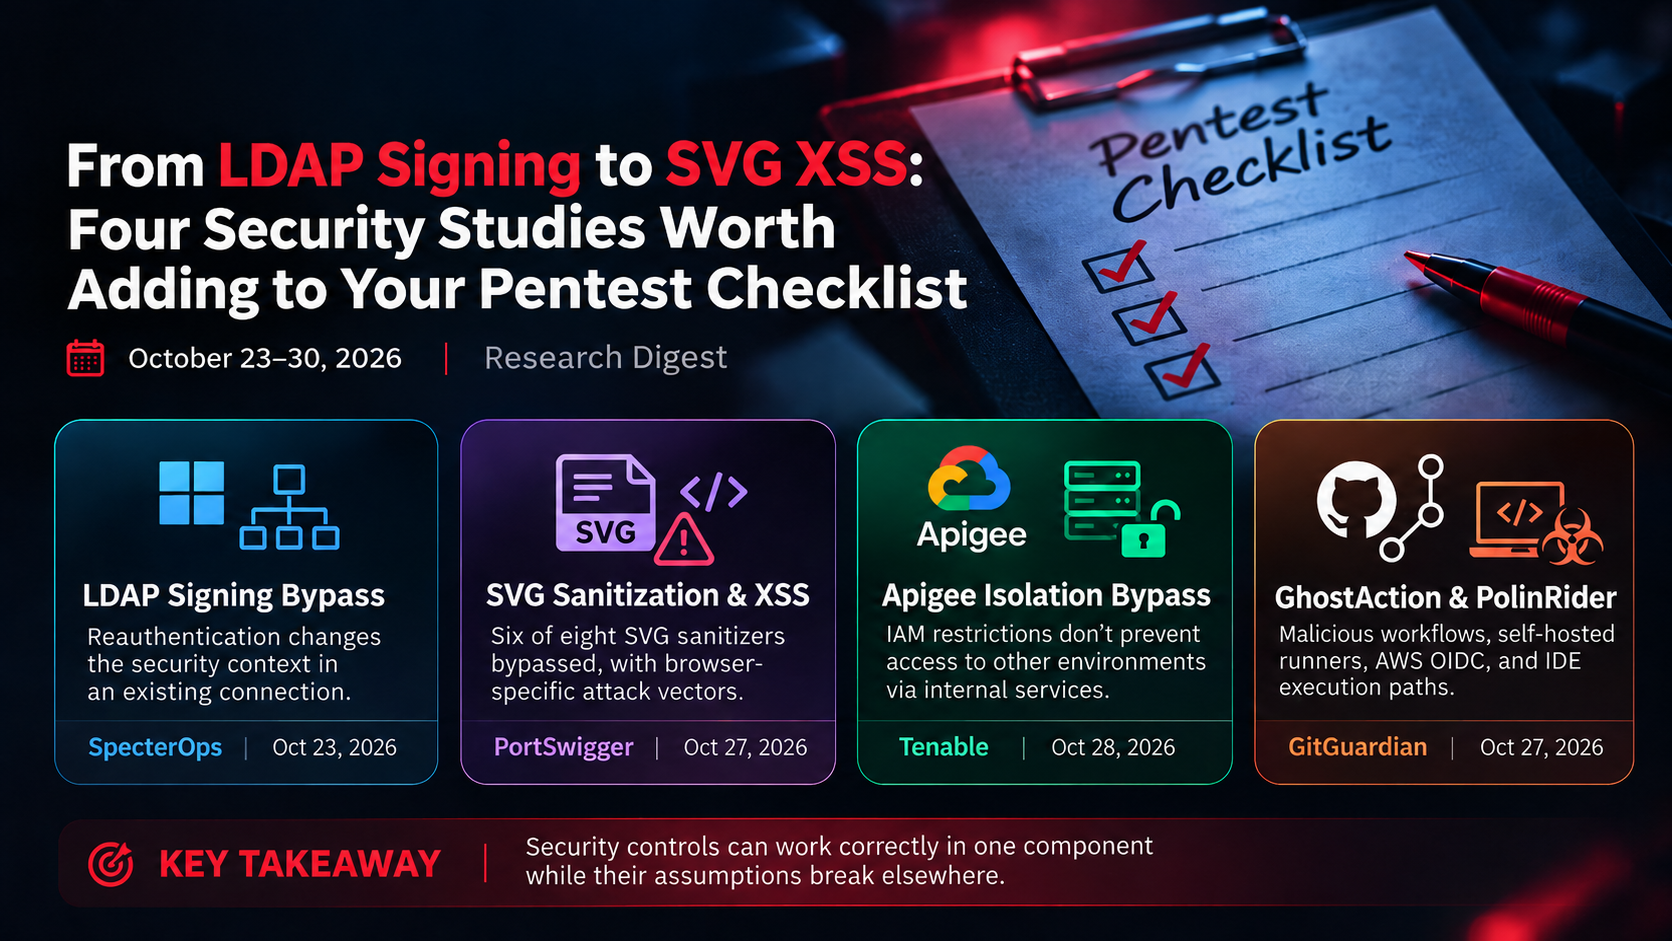
Four new cybersecurity studies reveal security control weaknesses involving LDAP signing bypasses, SVG sanitization and XSS, Google Cloud Apigee environment isolation, and GhostAction supply chain attacks. Explore the technical findings, exploitation prerequisites, and practical penetration testing lessons from SpecterOps, PortSwigger, Tenable, and GitGuardian.

Continue reading: From LDAP Signing Bypass to SVG XSS: Four Security…
Node2Shell (CVE-2026-111497) - We built an open-source scanner and a hands-on lab

Node2Shell (CVE-2026-111497) - We built an open-source scanner and a hands-on lab

RedSide Security October 30, 2026 Tools & Technology 591 views

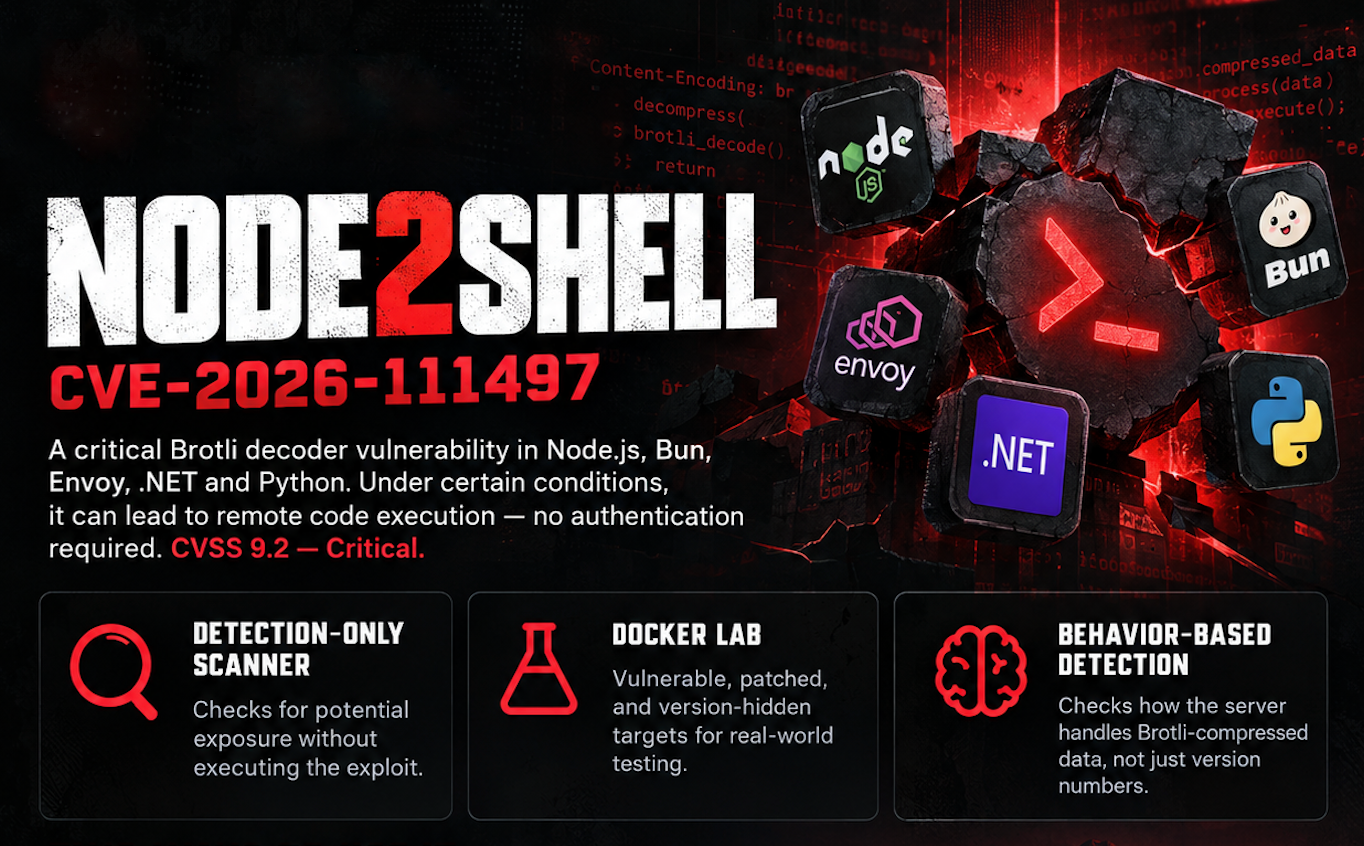
RedSide Security has released an open-source Node2Shell (CVE-2026-111497) scanner and Docker-based testing lab. The toolkit features non-destructive, behavior-based detection, vulnerable and patched test environments, and a lightweight Python implementation to help security teams investigate potential exposure to the critical Brotli vulnerability.

Continue reading: Node2Shell (CVE-2026-111497) - We built an open-so…
PHP2Shell: Two Critical PHP Vulnerabilities Allow Unauthenticated Remote Code Execution

PHP2Shell: Two Critical PHP Vulnerabilities Allow Unauthenticated Remote Code Execution

RedSide Security October 21, 2026 CVE 580 views

PHP has released emergency security updates for two critical PHP2Shell vulnerabilities, CVE-2026-109618 and CVE-2026-109619, both rated CVSS 9.2. The flaws affect PHP memory management and could allow unauthenticated remote code execution on vulnerable web servers. Administrators are urged to upgrade to patched PHP versions immediately.

Continue reading: PHP2Shell: Two Critical PHP Vulnerabilities Allow …
 Atlassian CVE-2026-21589: Critical File Access Vulnerability Affects 8 Data Center Products

Atlassian CVE-2026-21589: Critical File Access Vulnerability Affects 8 Data Center Products

RedSide Security October 06, 2026 CVE 346 views

Atlassian has disclosed critical vulnerability CVE-2026-21589 affecting eight self-hosted Data Center products, allowing unauthenticated attackers to read specific files from application root directories. Rated CVSS 9.3, the flaw affects Jira, Confluence, Bitbucket, Bamboo, Crowd, Crucible, and Fisheye, with Atlassian urging customers to patch immediately.

Continue reading: Atlassian CVE-2026-21589: Critical File Access Vu…