Cloud Security — Cybersecurity News

Latest News

Iran-Linked DarkBlinders Hits Israeli Figure and Kurdish Government Cloud

Iran-Linked DarkBlinders Hits Israeli Figure and Kurdish Government Cloud

RedSide Security November 02, 2026 Threat Intelligence 77 views

An Iran-aligned group tracked as DarkBlinders compromised a high-profile Israeli individual and a Kurdistan Regional Government cloud environment between August and October 2026, according to Dream Research Labs.

Continue reading: Iran-Linked DarkBlinders Hits Israeli Figure and K…
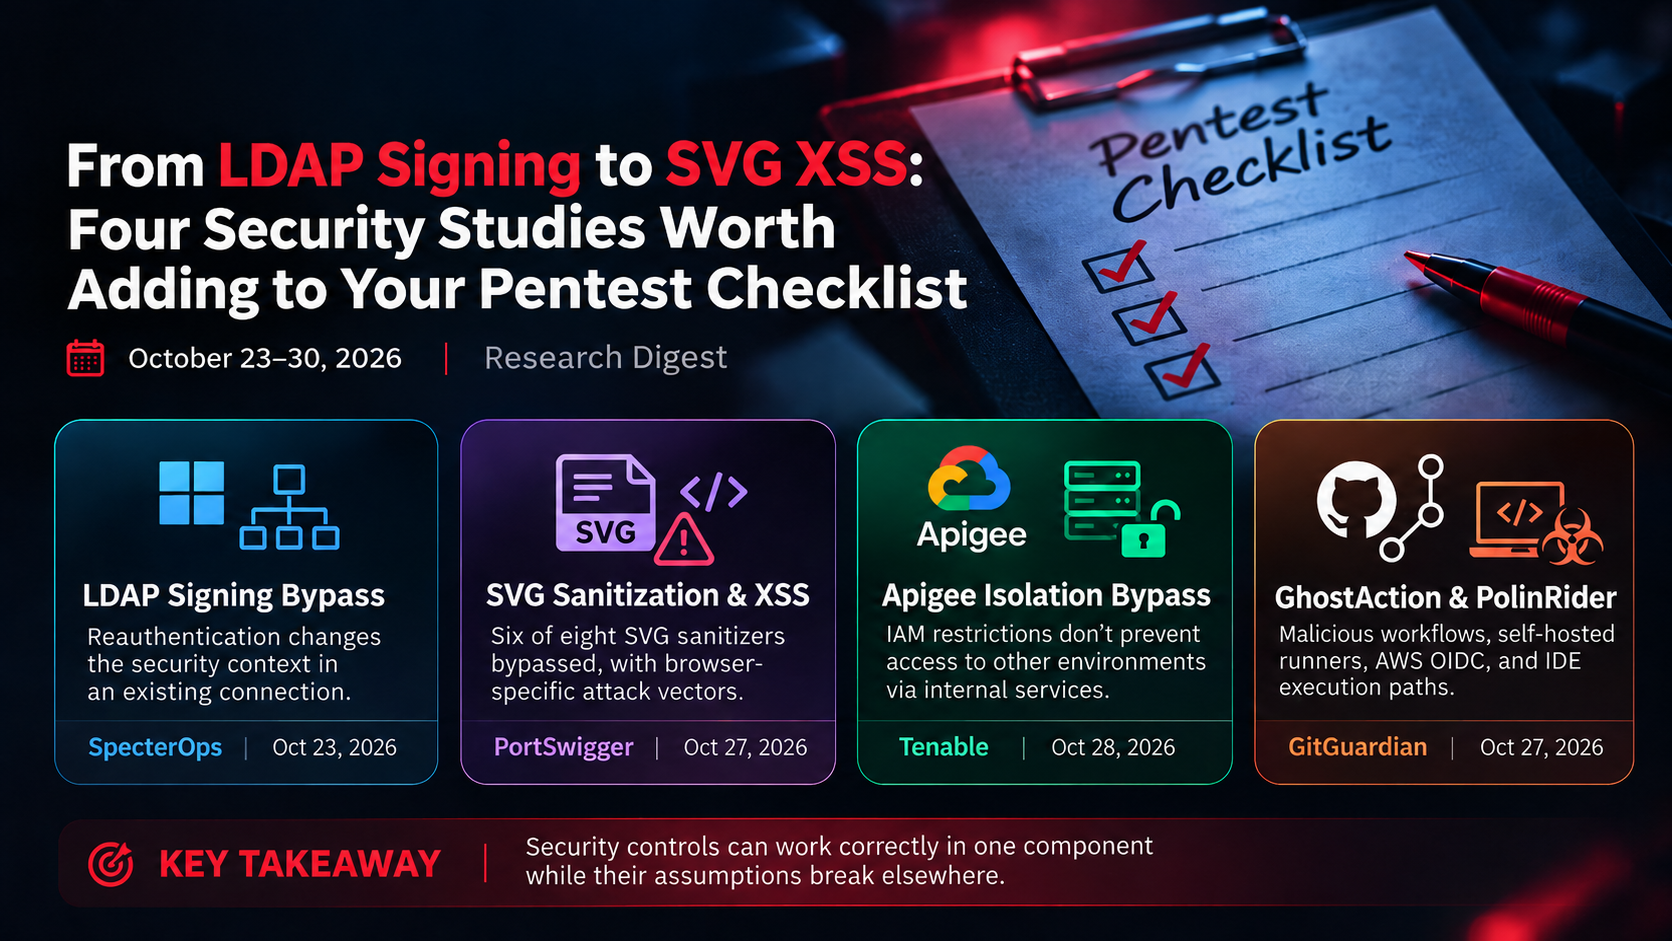
From LDAP Signing Bypass to SVG XSS: Four Security Research Studies Worth Adding to Your Pentest Checklist

From LDAP Signing Bypass to SVG XSS: Four Security Research Studies Worth Adding to Your Pentest Checklist

RedSide Security October 31, 2026 Penetration Testing 158 views

Four new cybersecurity studies reveal security control weaknesses involving LDAP signing bypasses, SVG sanitization and XSS, Google Cloud Apigee environment isolation, and GhostAction supply chain attacks. Explore the technical findings, exploitation prerequisites, and practical penetration testing lessons from SpecterOps, PortSwigger, Tenable, and GitGuardian.

Continue reading: From LDAP Signing Bypass to SVG XSS: Four Security…
McDonald’s, Vodafone Hit by Azure Credential Theft Campaign Exposing Millions of Enterprise Records

McDonald’s, Vodafone Hit by Azure Credential Theft Campaign Exposing Millions of Enterprise Records

RedSide Security August 16, 2026 Data Leaks & Breaches 573 views

A threat actor known as TheHatman is allegedly selling employee directories stolen from major enterprises through compromised Azure and Microsoft Entra credentials. The campaign reportedly exposes millions of records, including corporate emails, employee details, reporting structures, service accounts, and administrator information, creating significant risks for spear-phishing, privilege escalation, and further network compromise.

Continue reading: McDonald’s, Vodafone Hit by Azure Credential Theft…
Researchers Find 282 iPhone AI Apps Exposing Paid AI Access Through Leaked API Credentials

Researchers Find 282 iPhone AI Apps Exposing Paid AI Access Through Leaked API Credentials

RedSide Security June 30, 2026 Vulnerability 240 views

Researchers analyzing 444 AI chatbot apps on iPhone found that 282 applications exposed paid AI access through leaked API keys, reusable tokens, or unsecured backend services. The findings highlight growing risks of LLMJacking attacks, where threat actors abuse stolen AI credentials to generate costly unauthorized model usage.

Continue reading: Researchers Find 282 iPhone AI Apps Exposing Paid …
GuardFall Bypass Lets Attackers Evade AI Coding Agent Safety Checks Using Decades-Old Shell Tricks

GuardFall Bypass Lets Attackers Evade AI Coding Agent Safety Checks Using Decades-Old Shell Tricks

RedSide Security June 30, 2026 Cybersecurity 289 views

Researchers have disclosed GuardFall, a shell command bypass technique that defeats safety protections in 10 popular AI coding agents. The flaw allows malicious commands to evade text-based filters and execute with user privileges, potentially exposing credentials, source code, and cloud infrastructure.

Continue reading: GuardFall Bypass Lets Attackers Evade AI Coding Ag…
Critical SimpleHelp Flaw Actively Exploited to Deploy TaskWeaver Loader and Djinn Stealer

Critical SimpleHelp Flaw Actively Exploited to Deploy TaskWeaver Loader and Djinn Stealer

RedSide Security June 30, 2026 Cybersecurity 208 views

Threat actors are actively exploiting CVE-2026-48558, a critical authentication bypass vulnerability in SimpleHelp RMM software, to deploy the TaskWeaver loader and Djinn Stealer. The malware targets cloud credentials, developer tools, AI platforms, cryptocurrency wallets, and enterprise infrastructure across Windows, macOS, and Linux systems.

Continue reading: Critical SimpleHelp Flaw Actively Exploited to Dep…