Red Team — Cybersecurity News

Latest News

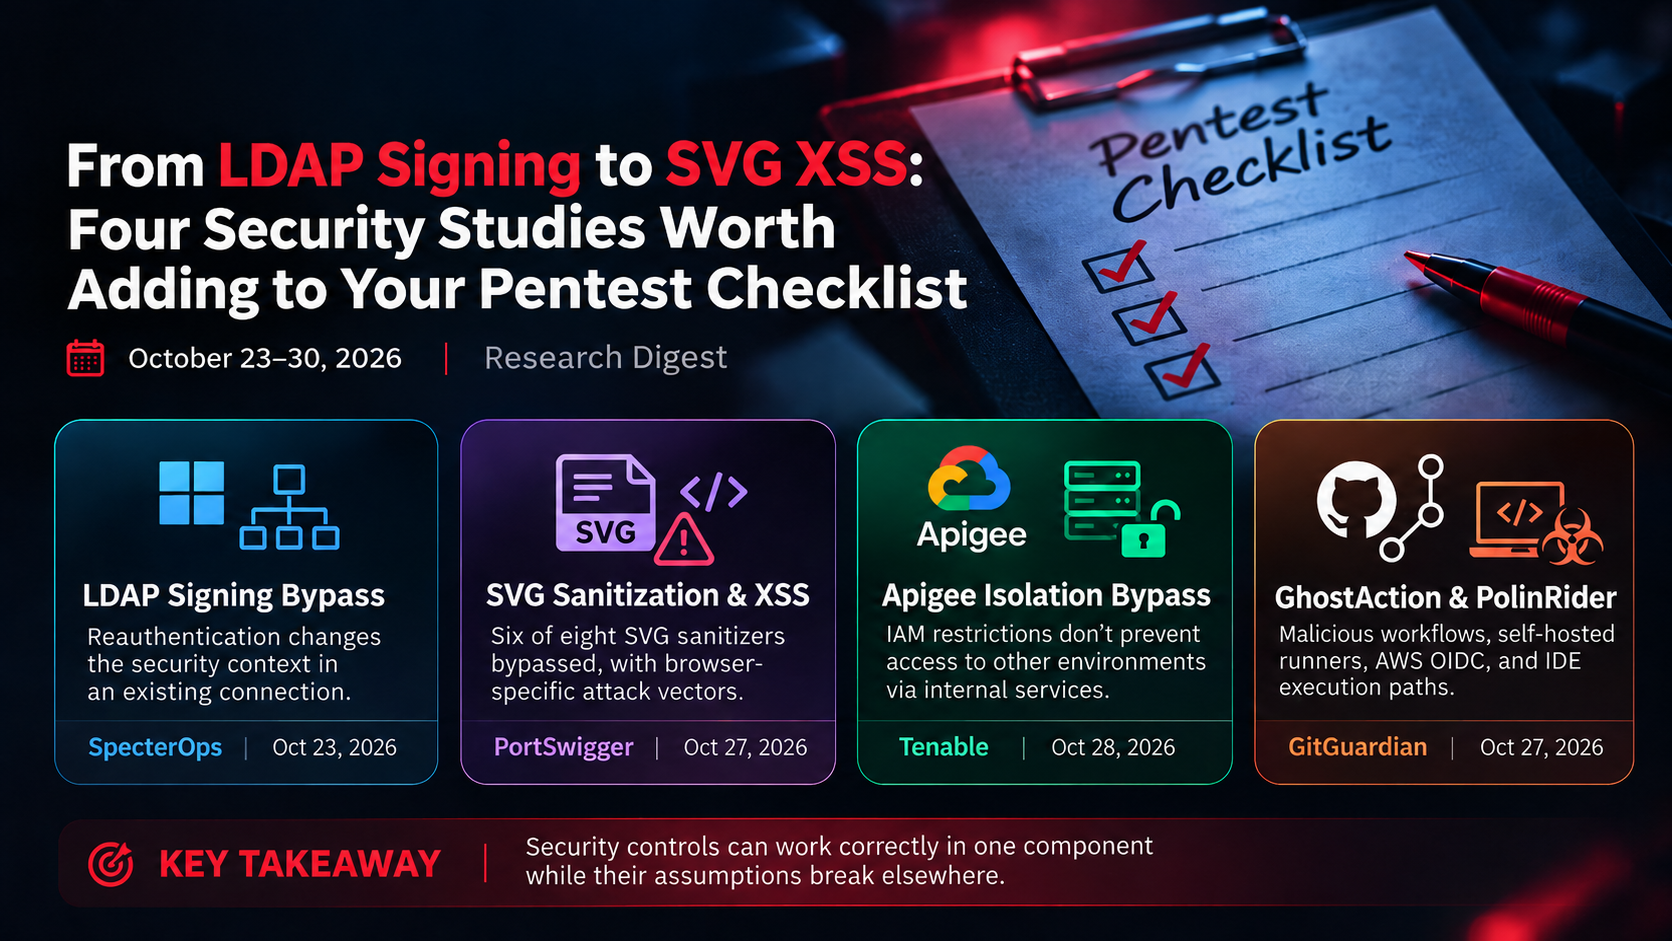
From LDAP Signing Bypass to SVG XSS: Four Security Research Studies Worth Adding to Your Pentest Checklist

From LDAP Signing Bypass to SVG XSS: Four Security Research Studies Worth Adding to Your Pentest Checklist

RedSide Security October 31, 2026 Penetration Testing 158 views

Four new cybersecurity studies reveal security control weaknesses involving LDAP signing bypasses, SVG sanitization and XSS, Google Cloud Apigee environment isolation, and GhostAction supply chain attacks. Explore the technical findings, exploitation prerequisites, and practical penetration testing lessons from SpecterOps, PortSwigger, Tenable, and GitGuardian.

Continue reading: From LDAP Signing Bypass to SVG XSS: Four Security…
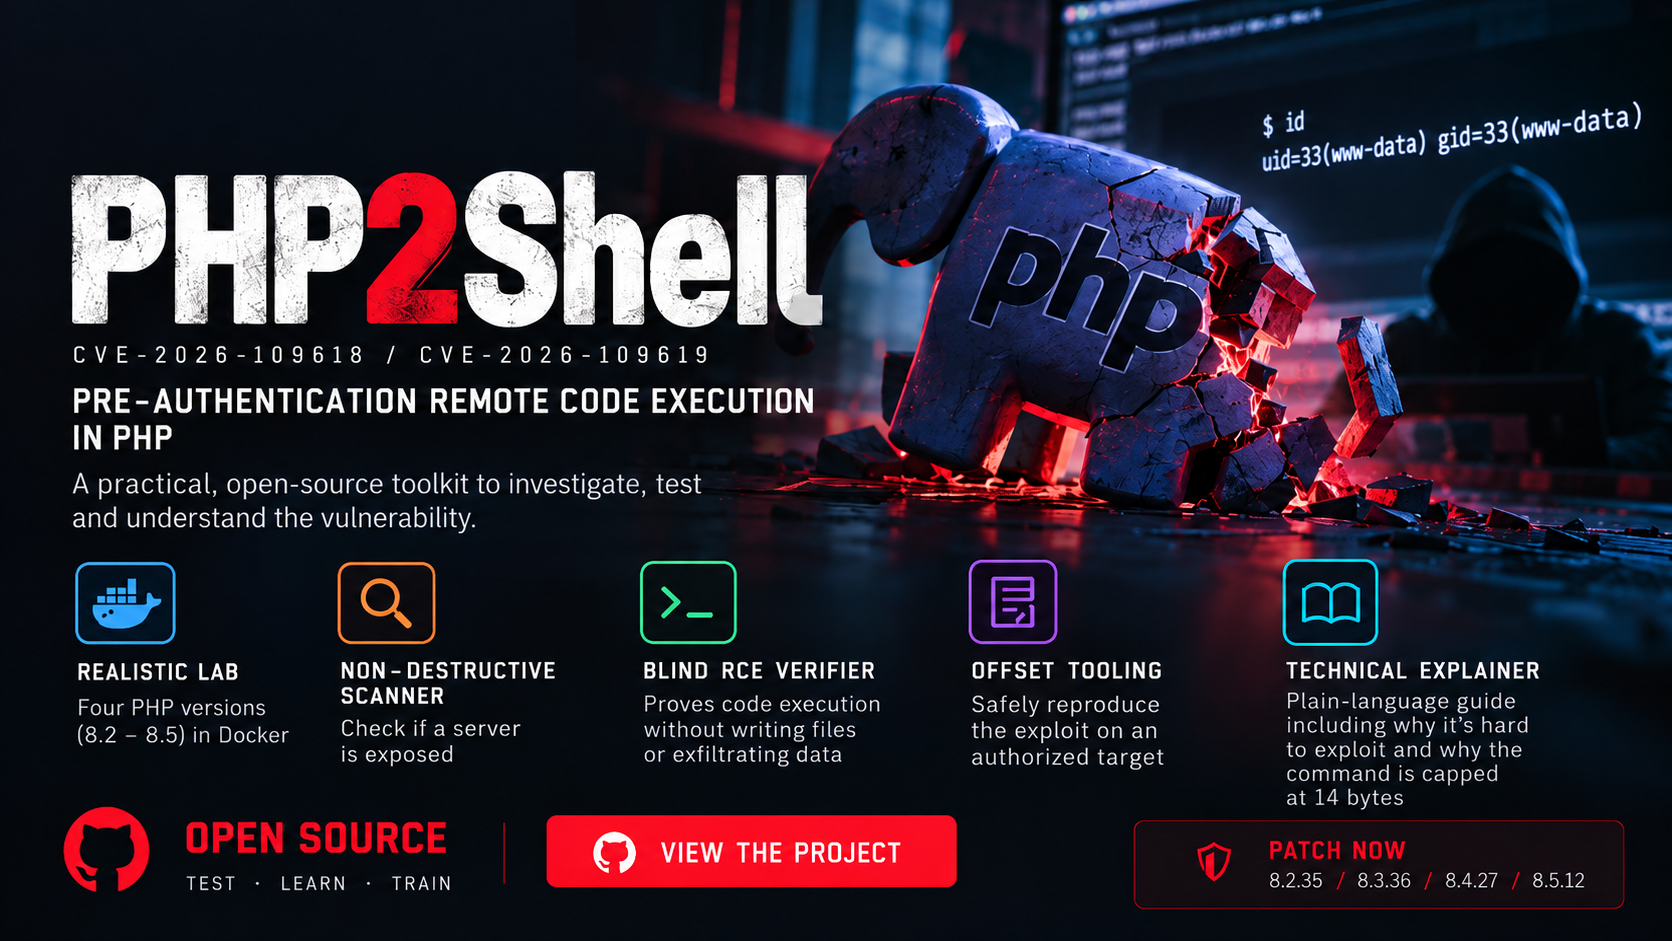
RedSide Security Releases Open-Source PHP2Shell Testing Lab, Scanner, and RCE Verifier

RedSide Security Releases Open-Source PHP2Shell Testing Lab, Scanner, and RCE Verifier

RedSide Security October 29, 2026 Tools & Technology 184 views

RedSide Security has open-sourced a PHP2Shell security research toolkit featuring a realistic Docker lab, non-destructive vulnerability scanner, blind RCE verifier, and binary offset tooling. The project helps security professionals investigate CVE-2026-109618 and CVE-2026-109619 through practical, authorized testing.

Continue reading: RedSide Security Releases Open-Source PHP2Shell Te…
PoC and Technical Details Released for SharePoint Remote Code Execution Vulnerability

PoC and Technical Details Released for SharePoint Remote Code Execution Vulnerability

RedSide Security July 08, 2026 Vulnerability 235 views

Researchers have released a working proof-of-concept exploit for CVE-2025-53770, a critical SharePoint Server remote code execution vulnerability. The flaw abuses XML schema imports and .NET deserialization gadgets to achieve code execution on vulnerable on-premises SharePoint deployments, increasing the risk of large-scale exploitation.

Continue reading: PoC and Technical Details Released for SharePoint …
Critical Fast-MCP-Telegram Vulnerability Allows Authentication Bypass via Path Traversal

Critical Fast-MCP-Telegram Vulnerability Allows Authentication Bypass via Path Traversal

RedSide Security July 07, 2026 Vulnerability 294 views

A critical authentication bypass vulnerability (**CVE-2026-52830**) in Fast-MCP-Telegram allows attackers to exploit path traversal flaws in Bearer token validation and gain unauthorized access to Telegram sessions. Users are strongly advised to upgrade to version 0.19.1 immediately.

Continue reading: Critical Fast-MCP-Telegram Vulnerability Allows Au…
Bad Epoll Linux Kernel Flaw Lets Attackers Gain Root Access on Linux and Android

Bad Epoll Linux Kernel Flaw Lets Attackers Gain Root Access on Linux and Android

RedSide Security July 04, 2026 Vulnerability 314 views

A newly disclosed Linux kernel vulnerability, Bad Epoll (CVE-2026-46242), allows unprivileged users to gain root access on Linux and Android systems through a race condition and use-after-free flaw in the epoll subsystem. With no workaround available, organizations are urged to deploy kernel patches as soon as they become available.

Continue reading: Bad Epoll Linux Kernel Flaw Lets Attackers Gain Ro…
DirtyClone Linux Kernel Vulnerability Enables Root Privilege Escalation

DirtyClone Linux Kernel Vulnerability Enables Root Privilege Escalation

RedSide Security June 29, 2026 Vulnerability 256 views

DirtyClone (CVE-2026-43503) is a newly disclosed Linux kernel privilege escalation vulnerability that allows local attackers to gain root access by abusing packet cloning and page-cache corruption. Researchers have released a working exploit, making immediate patching essential for affected Linux systems.

Continue reading: DirtyClone Linux Kernel Vulnerability Enables Root…
